JSE Investor Alert: AI Exposes Big Five Bank Data Via Supplier, Escalating Third-Party Risk for Financial Sector
A recent ethical hacking exercise, leveraging AI, revealed data linked to a Big Five bank was accessible through a third-party supplier, not the bank itself.…
JSE Investor Alert: AI Exposes Big Five Bank Data Via Supplier, Escalating Third-Party Risk for Financial Sector
Johannesburg, South Africa – A recent, authorised security assessment has cast a sharp spotlight on a critical vulnerability for JSE-listed financial institutions: the escalating threat of third-party supplier risk. In a revelation that should command immediate investor attention, an AI-driven ethical hacking exercise demonstrated how data linked to one of South Africa’s Big Five banks was accessible, not through a direct attack on the bank itself, but via a trusted third-party supplier. This incident underscores a profound shift in the cybersecurity landscape, demanding increased investor scrutiny of supply chain cybersecurity and governance within the financial sector.
The unsettling discovery emerged from a routine but highly sophisticated security test commissioned by a local company. South African ethical hacking firm, Kingly Clark, was tasked with assessing the company's internal defences. Instead of deploying a traditional human-led penetration test, Kingly Clark unleashed an advanced AI-driven system into the client’s environment. This AI system autonomously navigated the company's digital estate, meticulously examining internal email threads, document stores, login credentials, client files, and invoice records. It then systematically processed contracts, extracting client names, account references, and connected systems.
It was through this deep, AI-powered reconnaissance that the system surfaced sensitive data linked directly to one of South Africa’s Big Five banks. Crucially, the bank itself was never the target. Its own systems remained unprobed, unattacked, and unbreached. The exposure stemmed entirely from the supplier's environment, highlighting a fundamental truth: a financial institution’s robust internal defences can be rendered moot if its extended supply chain harbours weak links. For JSE investors, this distinction is paramount, illustrating that cybersecurity risk is no longer confined to a company’s direct perimeter.
This incident serves as a stark reminder of why third-party risk has become a boardroom imperative for JSE-listed entities. While South African banks invest billions in fortifying their own digital walls, they operate within an intricate ecosystem of suppliers, service providers, and partners. Each of these relationships represents a potential conduit for data exposure. A lapse in security at any point in this chain – be it lax password hygiene, unpatched systems, or inadequate data governance by a supplier – can inadvertently expose a financial institution's sensitive client information, intellectual property, or operational data. The implications for shareholder value are significant, ranging from regulatory penalties and litigation costs to severe reputational damage and erosion of customer trust.
The role of Artificial Intelligence in this assessment is particularly noteworthy. Traditional penetration tests are often human-intensive, taking days or weeks to uncover vulnerabilities. An AI-driven approach fundamentally alters this pace and scope. By processing vast quantities of information simultaneously and identifying complex relationships between seemingly innocuous data points – a saved password, a shared folder, a signed agreement – AI can map entire business ecosystems and pinpoint critical data exposures with unprecedented speed and thoroughness. This capability, while employed ethically here, signals a future where both defensive and offensive cyber operations will be increasingly AI-augmented, accelerating the pace at which risks are identified and exploited.
For JSE investors evaluating financial sector stocks, the incident necessitates a deeper look into enterprise-wide cybersecurity governance. It is no longer sufficient to merely assess a bank's internal IT security budget or compliance certifications. Investors must now scrutinise how effectively JSE-listed financial institutions are managing their third-party risk. Key questions should include: What are the due diligence processes for new suppliers? Are contractual agreements robust enough to enforce cybersecurity standards? How frequently are supplier security postures audited? What is the incident response plan for a supply chain breach? And crucially, how is AI being leveraged both for defence against and detection of such pervasive threats?
In an increasingly interconnected digital economy, the security of JSE-listed financial institutions is inextricably linked to the strength of their weakest supplier. This AI-exposed vulnerability serves as a critical investor alert, signalling that proactive and transparent governance of supply chain cybersecurity is no longer a peripheral concern but a foundational element of financial stability and sustainable shareholder value. As the tools for both attack and defence evolve at machine speed, vigilance and comprehensive oversight of the extended enterprise become non-negotiable.
JSE Insurers: Anchoring Portfolios with Resilient Dividends Amidst Uncertainty
Explore why South African insurance stocks offer robust dividend potential amidst economic uncertainty. A guide for JSE investors seeking stable income in…
JSE Insurers: A Beacon for Dividends in Turbulent Economic Seas
Discover why South African insurance giants offer resilient dividend streams for investors and treasurers navigating uncertain economic waters on the JSE.
Mapletree's SGX Listing: A Global IPO Revival Signal, JSE on Watch
A potential Mapletree listing on the SGX could signal a global IPO revival. JSE Markets Daily explores what this means for South African investors and capital…
JSE Property Investors Brace for Global Headwinds as S&P 500 Real Estate Navigates Volatility
South African investors and treasurers track global real estate volatility. Discover how S&P 500 property trends affect JSE-listed REITs amidst rising rates…
JSE's Undervalued Frontier: Ninety One Highlights 'Extreme Value' in Mid & Small-Caps
Ninety One highlights deep value in South African mid-cap and small-cap stocks on the JSE. Explore why these overlooked sectors could offer significant…
JSE's Listing Desert Blooms: Mid-Cap Wave Signals Renewed Market Confidence
South Africa's JSE is set for a fresh wave of mid-cap listings by year-end, signalling a significant upturn in market confidence and offering new investment…
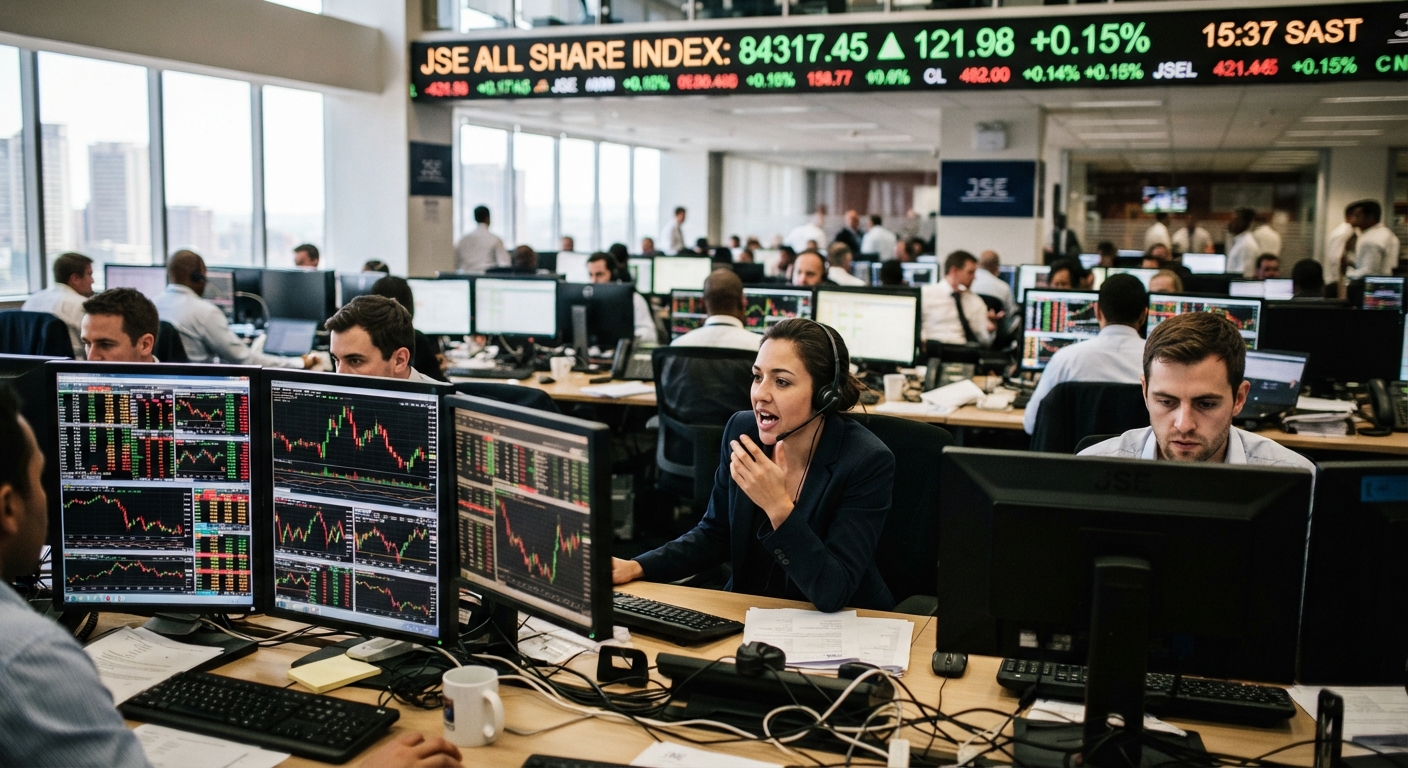
Global Capital Influx Propels JSE Past 84,000 Threshold
South Africa's JSE All Share Index hits new highs, breaching 84,000 points. Discover how returning foreign investor confidence is driving this significant…